FBI warns AI pen‑test tool ARTEX is fueling global cyber‑attacks
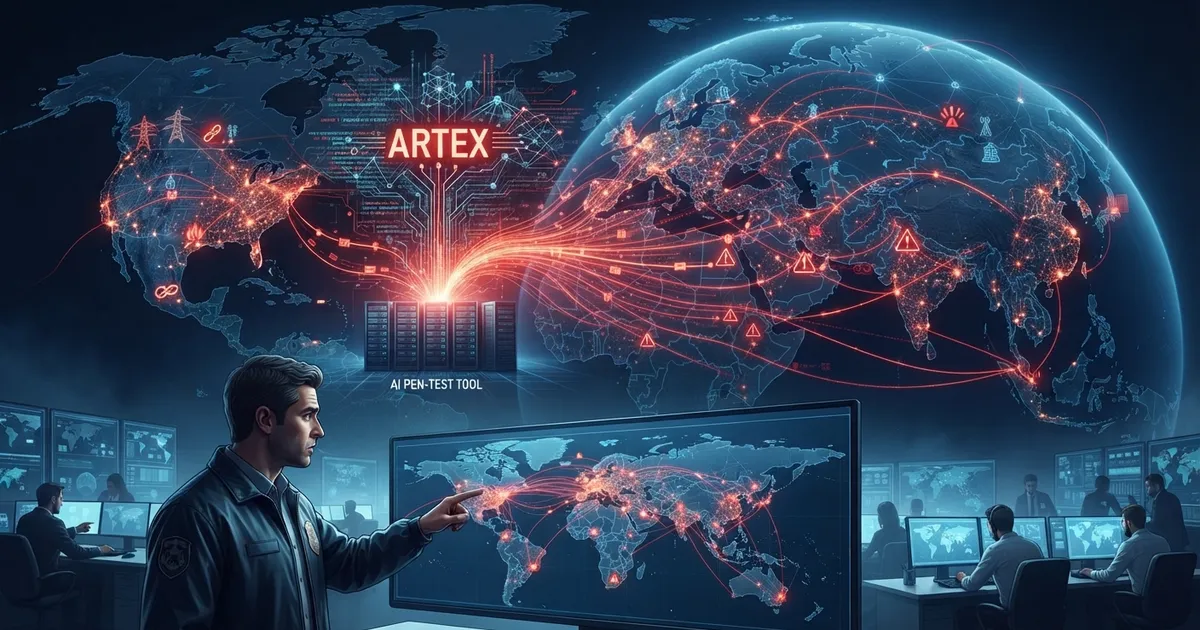
The FBI’s new FLASH advisory flags the open‑source Go framework ARTEX as a weapon for automated, AI‑driven intrusions across Microsoft 365 and beyond.
Deep-dive analysis, hands-on tutorials, and cutting-edge threat intelligence from industry practitioners.

The FBI’s new FLASH advisory flags the open‑source Go framework ARTEX as a weapon for automated, AI‑driven intrusions across Microsoft 365 and beyond.
40 result(s) for “Vulnerability”

Java4Shell is a memory‑corruption bug in OpenJDK’s AVX‑512‑accelerated Base64 decoder that enables remote code execution across many enterprise Java apps. Patches arrived on 2026‑11‑17.

Dark Reading warns of a possible Rails Active Storage/ImageMagick flaw that could let attackers write or read files, but the claim remains unverified.

BleepingComputer reports Anthropic researchers claim an exploit for a Linux kernel flaw that could give unauthenticated root on MPTCP servers, but no CVE or proof yet.

A researcher says unpatched Tailscale SSH bugs could let a compromised device gain root on other reachable servers; details remain unverified.

Researchers seized the insecure Time4Popcorn update domain, delivered a harmless payload and slashed update requests by 98%, protecting millions of Windows and macOS users.

PHP's security team warned of two CVSS 9.2 remote‑code‑execution flaws (CVE‑2026‑109618, CVE‑2026‑109619) and will push emergency updates on Oct 21.