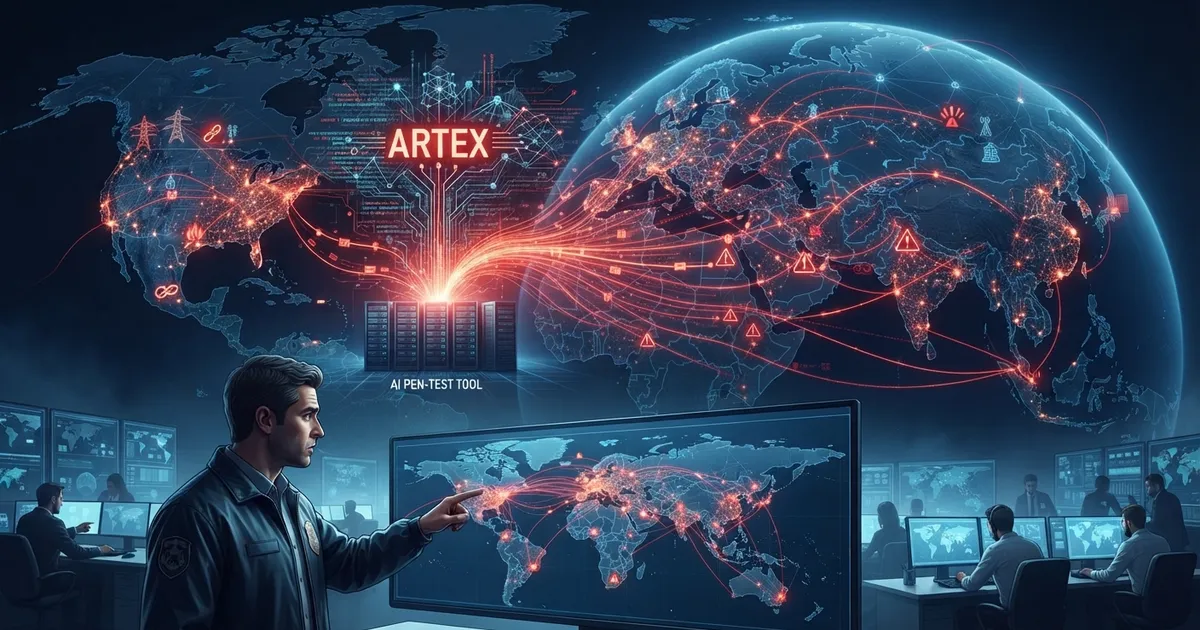
FBI warns AI pen‑test tool ARTEX is fueling global cyber‑attacks
The FBI’s new FLASH advisory flags the open‑source Go framework ARTEX as a weapon for automated, AI‑driven intrusions across Microsoft 365 and beyond.
Deep-dive analysis, hands-on tutorials, and cutting-edge threat intelligence from industry practitioners.

The FBI’s new FLASH advisory flags the open‑source Go framework ARTEX as a weapon for automated, AI‑driven intrusions across Microsoft 365 and beyond.
40 result(s) for “Vulnerability”

SiteGuard Server Edition’s statistics module contains a critical OS command‑injection flaw (CVE‑2026‑106931) that can grant root/SYSTEM access; a patch is now available.

Adobe’s BlockStrap flaw lets attackers run arbitrary code via email templates; a patch is available and no exploits have been seen yet.

A remote‑code execution flaw in PAN‑OS (CVE‑2026‑0322) was seen in the wild; patches released and CISA demands mitigation by Oct 17.

Over 1,400 flaws fixed on Oct 13, including 78 critical bugs and a Windows Shell zero‑day, while Microsoft pushes Windows 10 support to 2027.

Hackers exploit high‑severity stored XSS in two popular WordPress plugins to drop a fake “WP Smart Thumbnails” plugin, create hidden admin accounts and persist via secret login URLs.

Researchers see probes from a China Telecom IP hunting the session‑cookie signing flaw in Rejetto HFS, fixed in v3.2.1, with no confirmed exploits yet.