FBI warns AI pen‑test tool ARTEX is fueling global cyber‑attacks
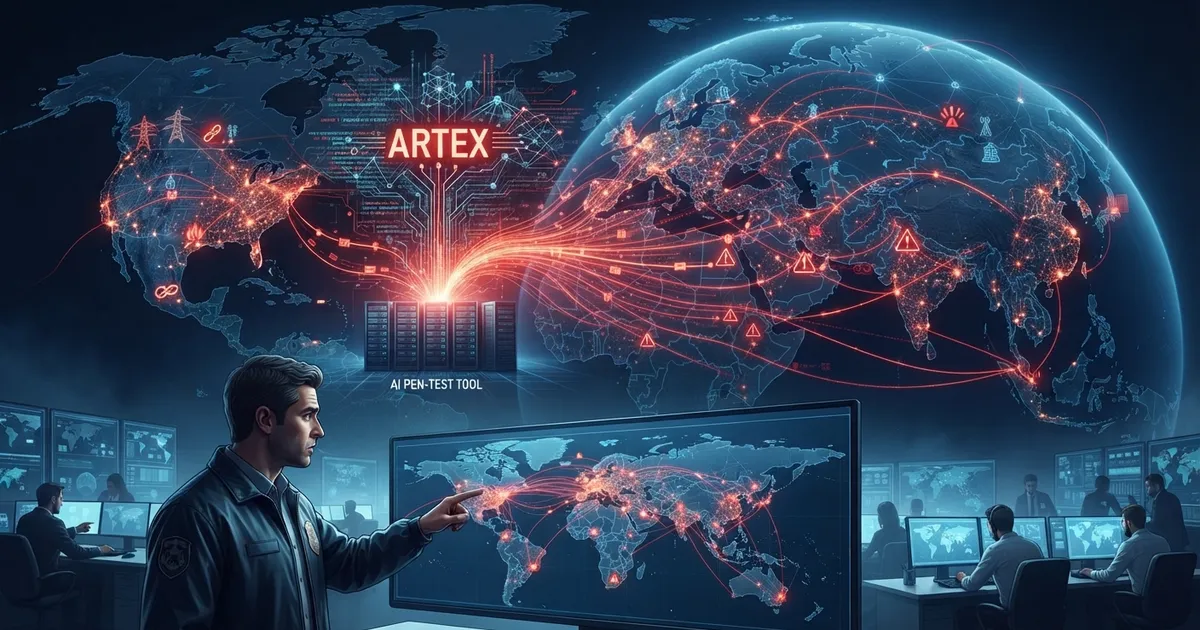
The FBI’s new FLASH advisory flags the open‑source Go framework ARTEX as a weapon for automated, AI‑driven intrusions across Microsoft 365 and beyond.
Deep-dive analysis, hands-on tutorials, and cutting-edge threat intelligence from industry practitioners.

The FBI’s new FLASH advisory flags the open‑source Go framework ARTEX as a weapon for automated, AI‑driven intrusions across Microsoft 365 and beyond.

PaperCut confirms attackers are weaponizing two critical CVEs (CVE‑2026‑82078, CVE‑2026‑81578) and has issued a second patch after the first proved insufficient.

Two high‑severity bugs in PaperCut NG/MF (CVE‑2026‑81578, CVE‑2026‑82078) prompted emergency patches; early reports suggest they could be chained for unauthenticated code execution.

A deserialization bug (CVE‑2026‑82222) in GiveWP up to v4.16.7.1 lets attackers run system commands on the host, even when WordPress registration is disabled.

Omdia analyst Theresa Lanowitz warns that autonomous AI tools can accelerate red‑team work but also introduce new safety and audit challenges.

PaperCut released Emergency Patch Release 2 after confirming exploitation of two critical flaws (CVE‑2026‑81578, CVE‑2026‑82078) in its NG/MF software.

A critical balance‑handling flaw in Cosmos’ EVM module (GHSA‑7g4w‑cg88‑2cq2) was exploited to steal funds from six blockchains in August 2026, forcing urgent upgrades.