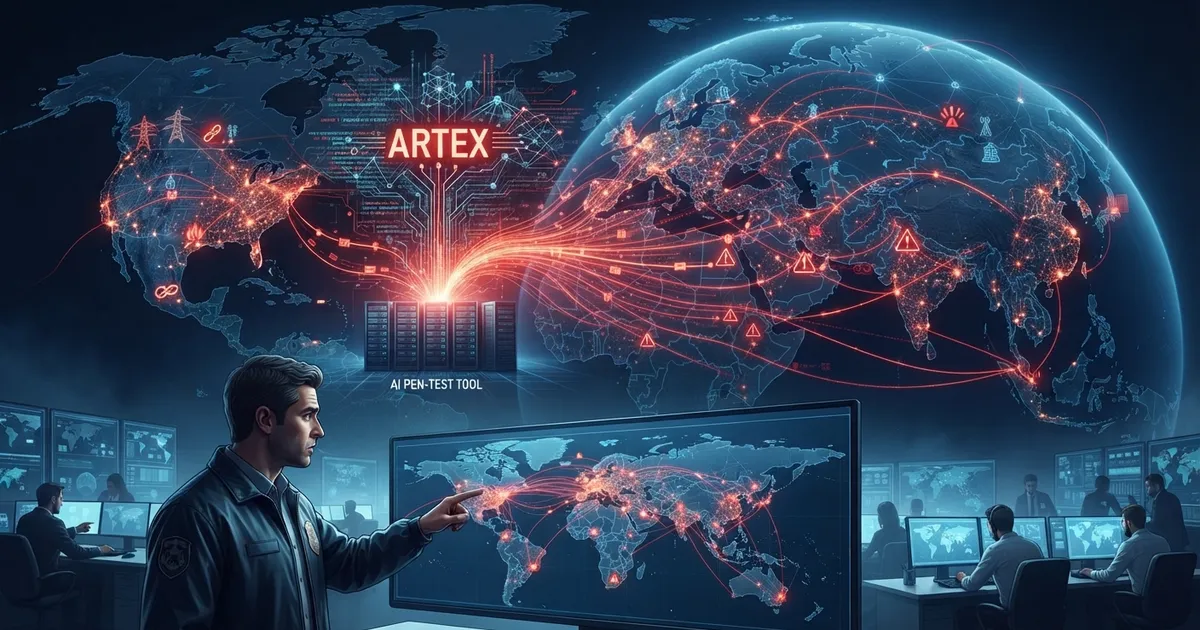
FBI warns AI pen‑test tool ARTEX is fueling global cyber‑attacks
The FBI’s new FLASH advisory flags the open‑source Go framework ARTEX as a weapon for automated, AI‑driven intrusions across Microsoft 365 and beyond.
Deep-dive analysis, hands-on tutorials, and cutting-edge threat intelligence from industry practitioners.

The FBI’s new FLASH advisory flags the open‑source Go framework ARTEX as a weapon for automated, AI‑driven intrusions across Microsoft 365 and beyond.
40 result(s) for “Vulnerability”

Acronis reports CVE‑2026‑87886 is being exploited in the wild and urges immediate patching of its cPanel/WHM and Plesk backup plugins.

CISA added CVE‑2026‑85706 to its actively exploited list, issuing a binding three‑day directive for federal agencies to patch the GitLab flaw.

CISA added five actively exploited CVEs for JFrog Artifactory, ConnectWise ScreenConnect and MikroTik RouterOS to its KEV catalog, with federal patch deadlines in mid‑September 2026.

Cisco confirms active exploitation of a critical authentication‑bypass bug in Secure FMC, CISA adds it to the KEV list, and hot‑fixes are now required.

CISA warns that two of the 973 vulnerabilities disclosed on September 2026 Patch Tuesday – CVE‑2026‑81963 and CVE‑2026‑85880 – are already being exploited. Federal agencies must patch by Sep 22.

A publicly disclosed unauthenticated code‑execution flaw in Magento Open Source and Adobe Commerce is being exploited to install a backdoor, with no vendor fix available.