Queens Public Library hit by ransomware, services crippled
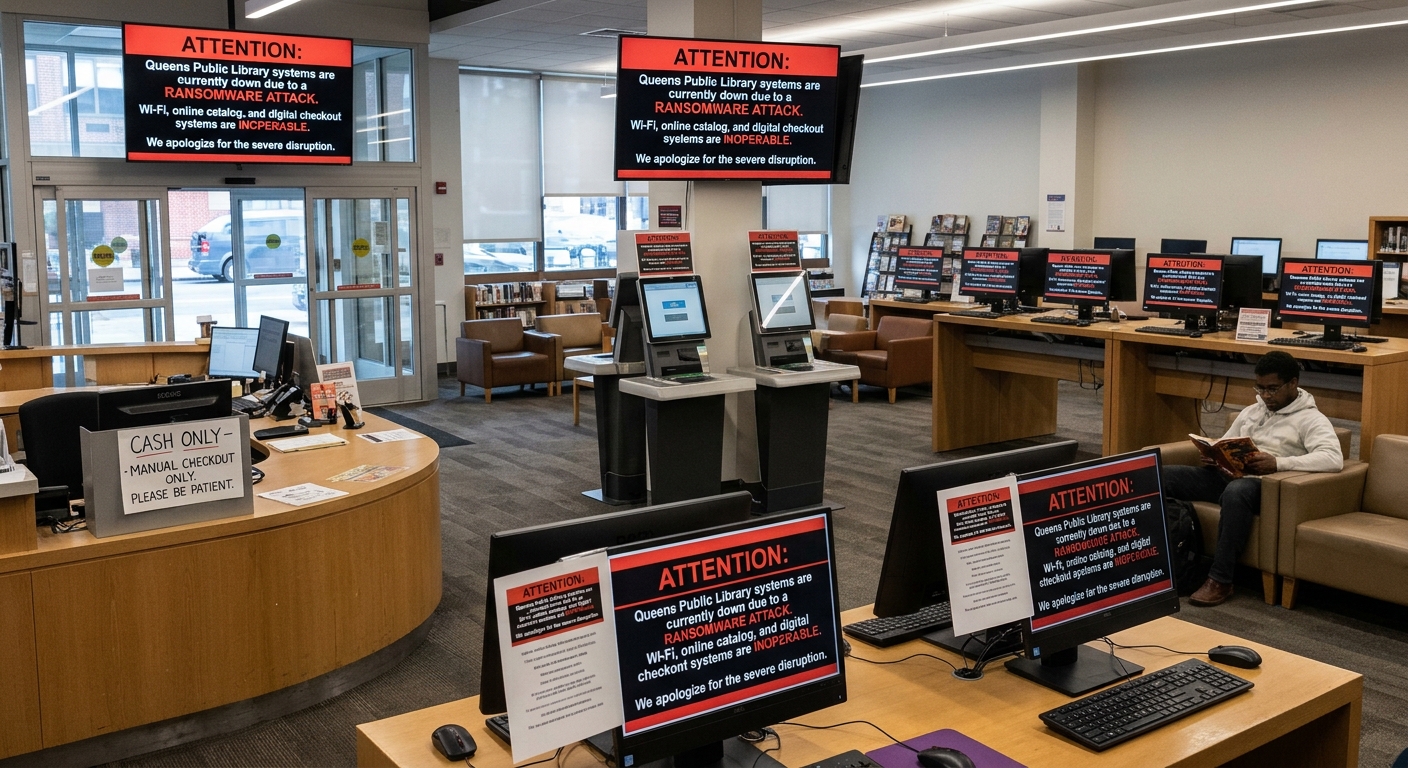
On Wednesday the city’s 66‑branch Queens Public Library announced that a ransomware strain had encrypted its internal systems, taking Wi‑Fi, checkout kiosks and the mobile app offline.
What went down
On‑site computers, self‑service check‑out and return machines, the public Wi‑Fi network, digital media platforms and the library’s mobile application all stopped working. The disruption was visible to patrons within hours of the initial alert.
Why it matters
The library serves roughly 2.3 million residents. Even though the doors stayed open, many virtual programs and in‑person services that rely on the affected tech were unavailable, limiting access to information for a sizable urban population.
Who’s responding
QPL confirmed it is working with law‑enforcement and external cybersecurity experts to contain the breach and begin recovery. No ransomware group has claimed responsibility yet.
Steps you can take
Organizations of similar size should treat this as a reminder to:
- Maintain immutable, offline backups of critical systems.
- Segment networks so that point‑of‑sale or checkout machines cannot be used to pivot into broader infrastructure.
- Enforce multi‑factor authentication for privileged accounts.
- Run regular vulnerability scans and apply patches promptly.
- Develop and test an incident‑response playbook that includes public‑facing services.
Keeping these basics in place can buy precious time if an attacker manages to encrypt your files.