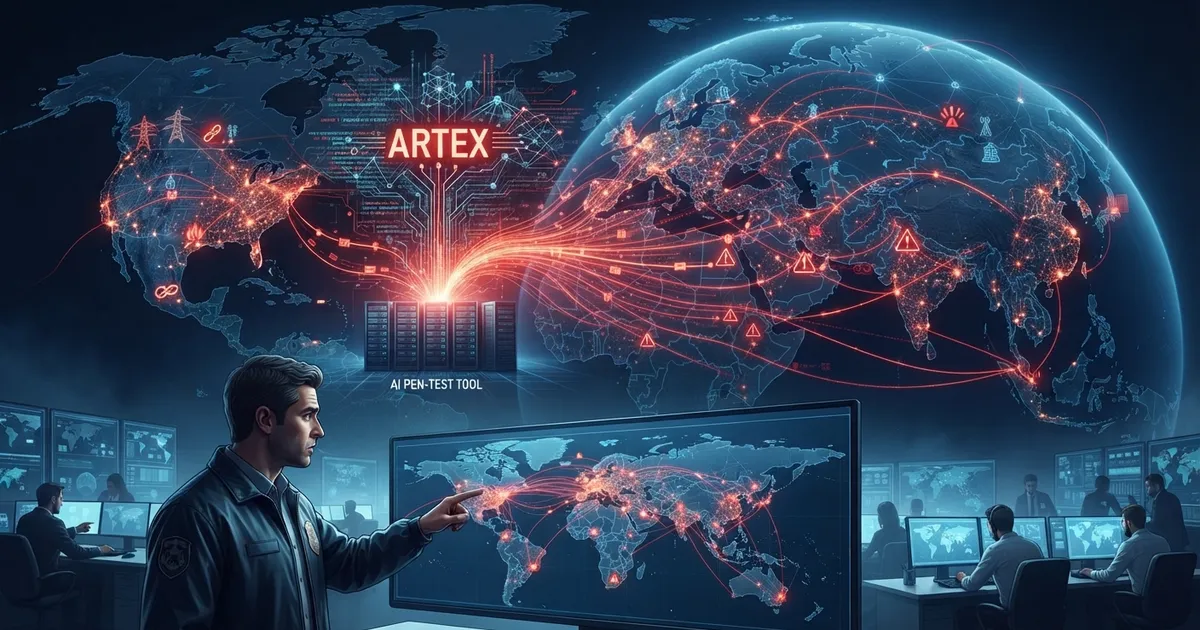
FBI warns AI pen‑test tool ARTEX is fueling global cyber‑attacks
The FBI’s new FLASH advisory flags the open‑source Go framework ARTEX as a weapon for automated, AI‑driven intrusions across Microsoft 365 and beyond.
Deep-dive analysis, hands-on tutorials, and cutting-edge threat intelligence from industry practitioners.

The FBI’s new FLASH advisory flags the open‑source Go framework ARTEX as a weapon for automated, AI‑driven intrusions across Microsoft 365 and beyond.

Hacktron leveraged Claude Opus 5 to combine a libheif RCE bug in Discourse with an OpenAI SSO flaw, briefly hijacking staff ChatGPT and Codex accounts and accessing an internal repo.

Vectra AI unveiled Ascent, a partner program aimed at expanding AI‑focused security services.

China‑origin APT‑Q‑95 has begun compromising Russian companies, using stolen VPN credentials to infiltrate Microsoft Exchange servers and install the GhostContainer backdoor.

Researchers uncovered 13 npm modules that pull the WeaselBiscuit JavaScript stealer, exfiltrating Chrome extension data on Windows, macOS and Linux.

Hacktron used Claude to auto‑write a remote‑code‑execution exploit for Discourse, then leveraged over‑permissive OpenAI sign‑in tokens to take over an employee’s ChatGPT account and push code to an internal repo.

Helpfeel says a hacker accessed Gyazo’s servers on Sep 11, 2026, stealing data on 23.6 million users and 490 million image‑metadata records.