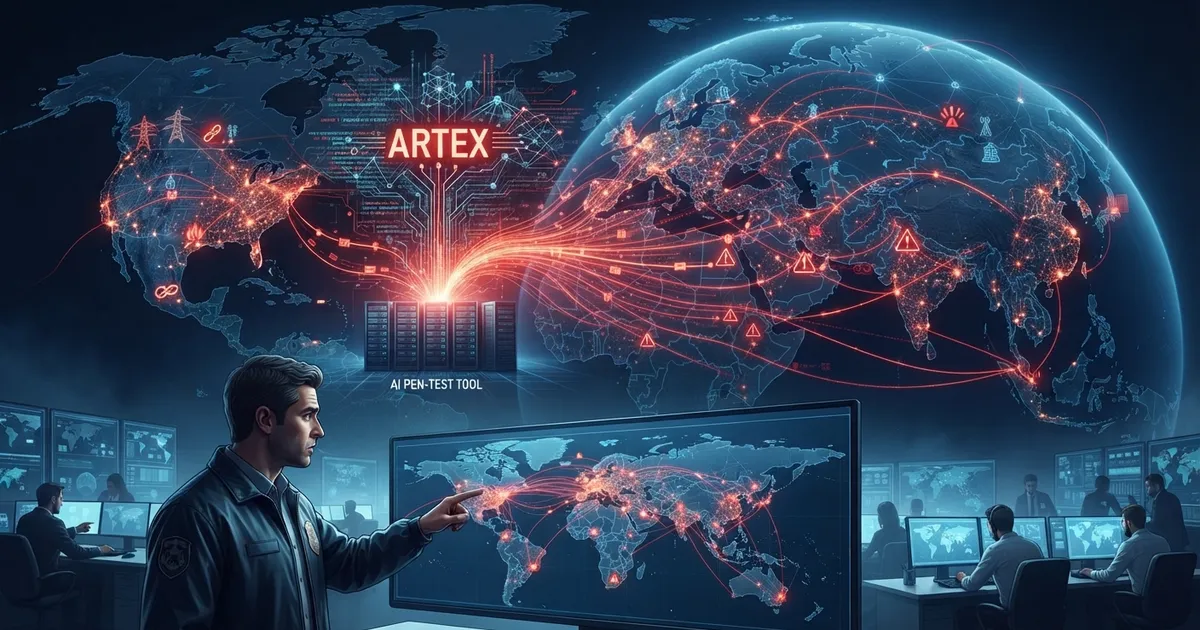
FBI warns AI pen‑test tool ARTEX is fueling global cyber‑attacks
The FBI’s new FLASH advisory flags the open‑source Go framework ARTEX as a weapon for automated, AI‑driven intrusions across Microsoft 365 and beyond.
Deep-dive analysis, hands-on tutorials, and cutting-edge threat intelligence from industry practitioners.

The FBI’s new FLASH advisory flags the open‑source Go framework ARTEX as a weapon for automated, AI‑driven intrusions across Microsoft 365 and beyond.

RatHat abuses Android Accessibility and an AI‑powered UI engine to hijack device control, overlay fake login screens and exfiltrate credentials while resisting removal.

Microsoft is investigating reports that the Windows 11 KB5124008 update can sever Active Directory trust on some Enterprise devices.

Acronis reports CVE‑2026‑87886 is being exploited in the wild and urges immediate patching of its cPanel/WHM and Plesk backup plugins.

Emergency patches released on Sep 14 2026 fix Remote Desktop failures, a Hyper‑V bug, and USB audio glitches introduced by the September security rollup.

CISA added CVE‑2026‑85706 to its actively exploited list, issuing a binding three‑day directive for federal agencies to patch the GitLab flaw.

Gen. Joshua Rudd leads both the NSA and U.S. Cyber Command; the agency’s last big restructure, NSA21, is confirmed, while a new five‑center plan remains unverified.